


In addition to the partnership with 247Venture, Verji Tech AS also announces the signing of a significant distribution agreement with 24SevenOffice.
Digital transformation has changed the way organisations operate. Across Norway, businesses and public institutions have invested heavily in modern platforms, cloud infrastructure, cybersecurity controls and digital workflows. Accounting firms manage financial information through specialised systems, municipalities deliver critical public services through digital platforms, and professional organisations rely on technology to manage increasingly complex information flows. However, while organisations have significantly improved how they store and process sensitive information, one important part of the digital ecosystem has received far less attention: how that information is communicated between people. The reality is that many confidential conversations still happen through communication channels that were not designed for managing sensitive data. A document containing financial records, personal information or confidential business details can still be shared through a simple email attachment, creating a gap between the security of the systems where information is stored and the security of how that information moves.
This gap is becoming increasingly important as organisations face growing expectations around GDPR compliance, data protection and information security. Protecting personal data is not only about having secure databases or access-controlled systems. Organisations are responsible for protecting personal data throughout its entire lifecycle, including when it is shared with colleagues, customers, suppliers and other external parties. According to Datatilsynet, Norway recorded 3,191 personal data breach notifications in 2024, representing a 13% increase compared to the previous year. Around 37% of these reported breaches involved personal information being sent to the wrong recipient, making communication mistakes one of the most common causes of data exposure. These incidents highlight an important reality: many data protection failures are not caused by a lack of cybersecurity investment, but by everyday communication practices where human error and uncontrolled information sharing remain significant risks.
For organisations handling confidential information every day, this challenge is particularly relevant. Accounting firms exchange financial statements, payroll information, tax documentation and sensitive client records. Law firms manage confidential legal matters, contracts and personal information where privacy is fundamental to maintaining trust. Municipalities and public organisations handle citizen information where even a small communication mistake can have serious consequences for individuals and institutions. In all these environments, communication is not simply an operational activity; it is part of the organisation’s responsibility to protect information. Yet many organisations still depend on workflows where employees must manually decide whether information is sensitive enough to require additional protection, whether a recipient is correct, or whether an attachment should be shared through another method. This places a significant responsibility on individuals and creates unnecessary exposure in processes that happen thousands of times every day.
The increasing sophistication of cyber threats makes this challenge even more complex. Phishing and impersonation attacks continue to target communication channels because they exploit the way people naturally interact with messages and information. A convincing email can appear to come from a trusted customer, colleague or supplier, making it harder for employees to distinguish legitimate communication from malicious attempts. While organisations continue to improve security awareness and employee training, relying only on human judgement is no longer enough. Secure communication needs to become part of the technology environment itself, where protection is built into the way people exchange information rather than added only after a risk has already been identified.
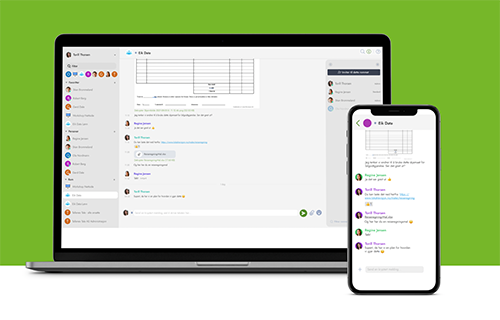
This is where secure communication platforms are becoming an important part of modern data protection strategies. GDPR-compliant communication requires organisations to consider not only the policies they have in place but also the tools employees use every day. A secure communication environment should help organisations control access, protect information during exchange, reduce unnecessary exposure and create a more structured way of managing sensitive conversations. Verji provides an end-to-end encrypted communication platform designed to support GDPR-compliant handling of sensitive information and the requirements of organisations operating under Norway’s Personal Data Act. The platform enables secure conversations, controlled communication rooms, encrypted file exchange, authentication and BankID-supported signing, helping organisations create a safer environment for communicating with clients, citizens and external stakeholders.
With roots dating back to 2017, Verji has developed its platform around the practical needs of organisations where confidentiality is essential, including accounting firms, auditors, law firms, municipalities and other professional service providers.
Today, more than 200 organisations use Verji to manage secure communication with customers and external parties.
The goal is not to replace every existing communication method, but to provide organisations with a trusted alternative when information requires stronger protection. GDPR compliance cannot depend only on policies, employee awareness or annual security training. Those elements remain important, but the communication tools used every day must also support organisations in protecting sensitive information by design.
As digital transformation continues, the next stage of data protection will not only be about securing where information is stored. It will also be about securing how information is shared. Organisations that handle confidential data need to look beyond traditional security boundaries and consider the complete journey of information — from creation to communication. Because sensitive information deserves protection at every stage, including the conversations built around it.